Vooki Pro
DAST for Web Applications & REST APIs
Vooki Pro helps security teams find, validate and fix vulnerabilities faster — a DAST desktop app for web applications and REST APIs, with every scan running locally on your own machine.
Every feature unlocked for 7 days · No credit card required
Audit-ready coverage
Mapped to the standards your auditors ask for.
Web application security & API coverage
OWASP TOP 10
Built local-first, from the ground up
Every scan and every AI-assisted analysis runs on your own machine — nothing about your target or findings has to leave your network to get results.
Local-First Testing
Findings and the HTTP evidence behind them live in a local SQLite database on your own machine, not a vendor cloud.
On-Device AI
ThreatLens runs on-device — no scan content is ever sent to a third-party AI service.
Web + REST API DAST
One tool, one workflow, for both web applications and the REST APIs behind them — no separate scanner to license and learn.
From target to retested fix
One desktop app, four stages — the same workflow for a web application or a REST API, start to finish.
Discover
Map the real attack surface before a scan starts — a quick seed, a full crawl, a recorded browser session, or a hybrid of the two, with an optional headless pass that captures background XHR/API endpoints. Depth, URL and time budgets keep discovery scoped to what you choose.
Scan
Test web applications and REST APIs with the same engine. Import an OpenAPI v2/v3 spec, a Postman collection or a HAR file, or build requests by hand in the workspace. Authenticate with form login, tokens, OAuth2 or a recorded session so the scan sees what a logged-in user sees, then run a built-in or custom policy at the speed you choose, from stealth to aggressive.
Analyze & Retest
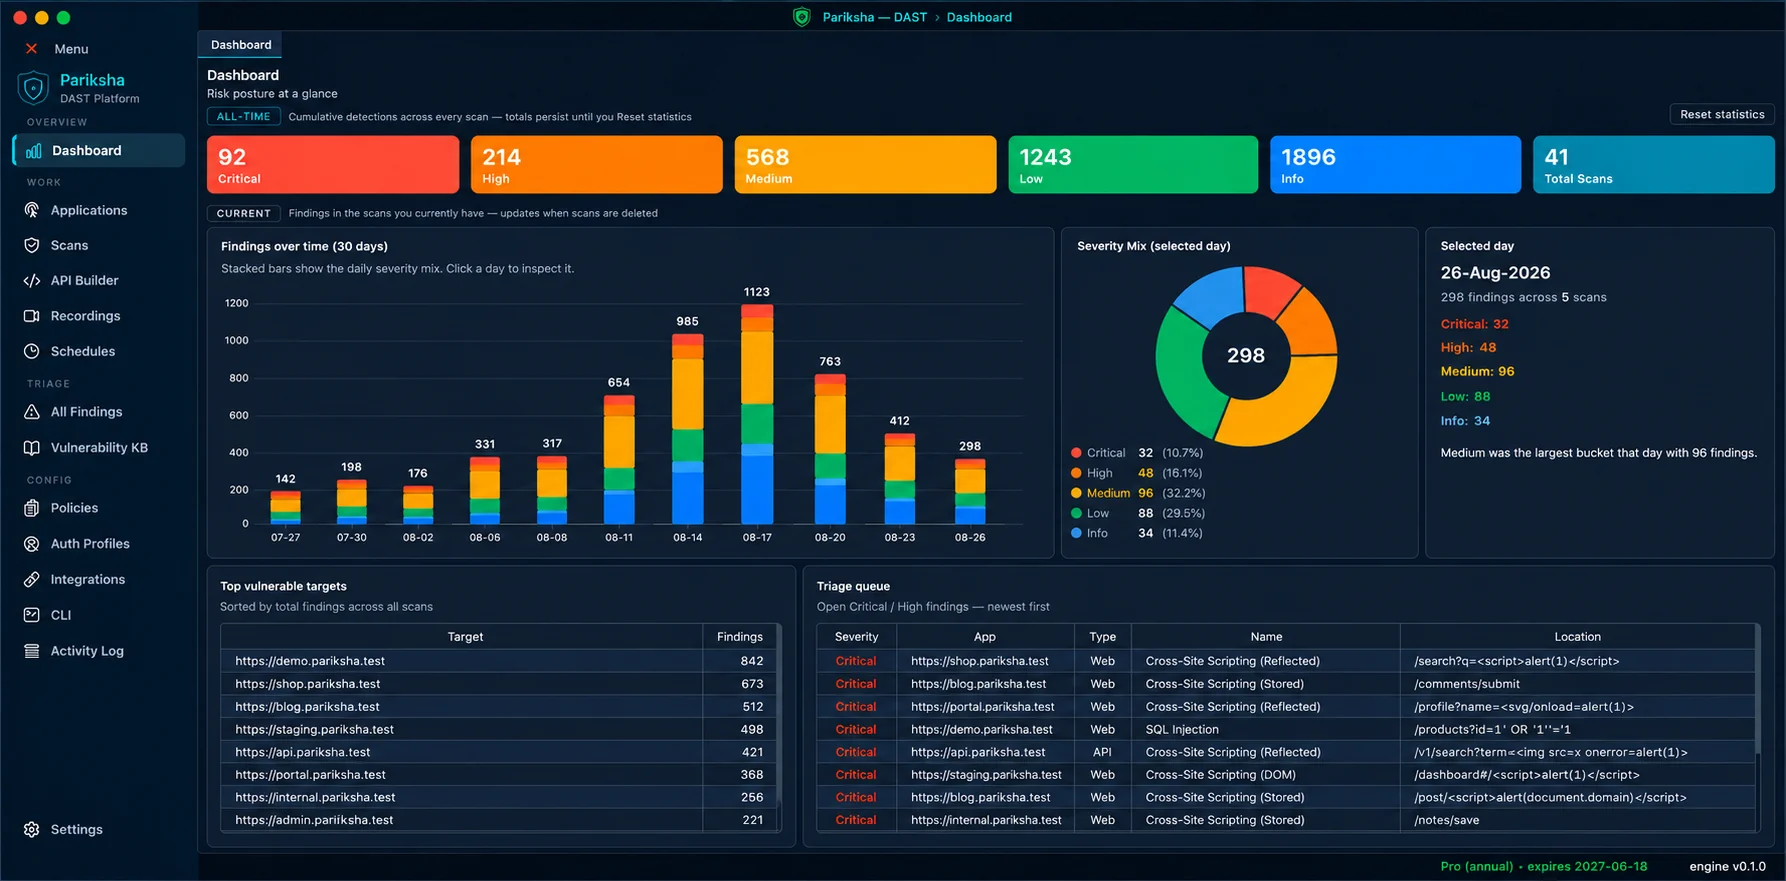
Browse findings across every scan and read the full HTTP request and response with the injected payload highlighted. ThreatLens, an on-device AI model, triages findings and surfaces patterns the deterministic checks miss. Mark a fix, and the same detector that raised the finding retests it and returns a verdict.
Automate & Integrate
Run scans on a cron expression or a simple interval, or trigger them headlessly from CI/CD with vooki-pro-cli — export any wizard-configured scan as a JSON config, set a severity threshold, and let the pipeline fail on its own. File findings straight into Jira, GitHub Issues, Linear, GitLab or Azure DevOps, and send alerts to Slack or any webhook.
Built around how you already work
AppSec Teams
Run scheduled scans across every application you own, and triage findings from one place instead of chasing each team for access.
VAPT / Pentest Teams
Point Vooki Pro at a client's environment under NDA without a public target or a data-processing agreement — the scan never leaves your machine.
Developers
Retest a fix in seconds with the exact HTTP evidence that raised it, instead of waiting on the next scheduled assessment.
API Security Teams
Import an OpenAPI spec, Postman collection or a capture, and test for BOLA, BFLA and mass assignment without hand-building requests.
Broad, categorized coverage
Active attack checks plus version and outdated-component fingerprint checks, organized into categories and all selectable individually when you build a custom policy.
Injection & XSS
SQL and blind SQL, NoSQL, XXE, XPath, LDAP, OS command, SSTI, SSI, CRLF, host header, GraphQL, expression language, ORM, HPP and XSLT — plus reflected, stored, DOM, mutation, SVG and header-based cross-site scripting.
29 checksAccess Control & Auth
IDOR, BFLA, path traversal, forced browsing, privilege escalation and method override, alongside default credentials, user enumeration, weak password policy and the full JWT family — alg none, weak alg, algorithm confusion, jku and kid.
24 checksAPI Security
BOLA, BOPLA, BFLA, mass assignment, unrestricted resource consumption, GraphQL introspection and DoS, API misconfiguration, inventory and versioning issues — mapped to the OWASP API Top 10.
12 checksHeader, cookie, CORS, SRI and outdated-dependency issues are consolidated into one finding per host, origin, cookie or dependency — not one per crawled URL.
Timing-based attacks run in a separate second pass that skips anything already confirmed, so network jitter doesn't turn into a critical finding.
WAF and CDN detection, auth-health checks and session-expiry detection warn you when a scan is being blocked or the session died halfway through.
What Vooki Pro is — and isn't
Knowing what a tool doesn't do is as useful as knowing what it does.
- Web application DAST
- REST API security testing
- Authenticated security testing
- Vulnerability detection and reporting
- Automated retesting
- On-device AI-assisted analysis
- Scheduling and CI/CD via the CLI
- SAST (static code analysis)
- SCA (software composition analysis)
- A network vulnerability scanner
- A mobile APK scanner
- Manual-pentest tooling — no proxy interceptor, repeater or fuzzer
Reports your team and auditors can use
Export to PDF, HTML, Word (DOCX) or JSON. Standard reports carry an executive summary, risk score and per-finding evidence; compliance reports map findings control by control against the frameworks shown above — a mapping capability, not a certification.
One app, one licence
Start with a 7-day full-feature trial, then activate a licence key. Licensed per domain — one slot covers a domain and every subdomain under it — not per seat, not per scan.
Every feature unlocked for 7 days, so you can evaluate the real thing before you buy.
For continuous, scheduled testing all year.
Buy NowFor continuous, scheduled testing all year.
Buy NowFor continuous, scheduled testing all year.
Buy NowFor continuous, scheduled testing all year.
Contact SalesCommon questions
Ready to scan
your first target?
Start your 7-day trial, point Vooki Pro at an application you're allowed to test, and see what a two-phase DAST run turns up.
Available for Windows, macOS, and Linux.